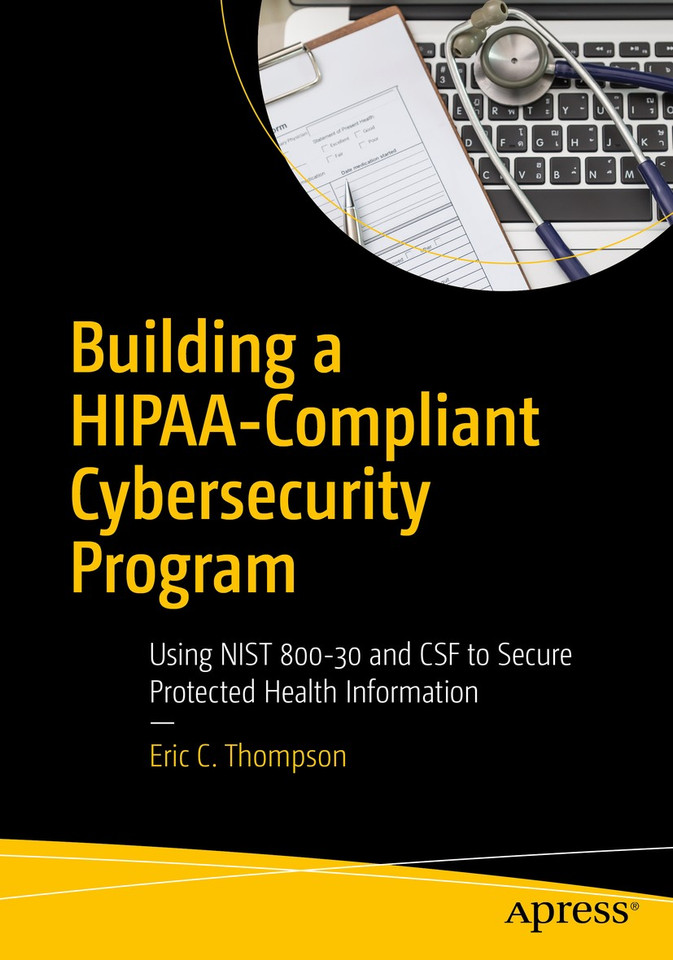
Building a HIPAA-Compliant Cybersecurity Program: Using NIST 800-30 and CSF to Secure Protected Health Information
$45.49 / copy at 25+ copies As low as $40.29 at 1,000+Your best volume price
Total $1,137.25
Format
The more copies, the less each one costs
Applied automatically in your cart. No code needed.
Turn this order into a program
Groups that order in bulk often pair the copies with something more. We handle the extras so you don't have to.
One address, many sites or individual recipients' homes, in the US and abroad.
Fulfillment options Pair it with a branded journalJournals with your logo or each reader's name, for the same group.
Branded journals Bring in a speaker
BookPal is partnering with Talezo to help you find and book authors, speakers and performers for your event.
BookPal × TalezoBuilding a HIPAA-Compliant Cybersecurity Program
Use this book to learn how to conduct a timely and thorough Risk Analysis and Assessment documenting all risks to the confidentiality, integrity, and availability of electronic Protected Health Information (ePHI), which is a key component of the HIPAA Security Rule. The requirement is a focus area for the Department of Health and Human Services (HHS) Office for Civil Rights (OCR) during breach investigations and compliance audits. This book lays out a plan for healthcare organizations of all types to successfully comply with these requirements and use the output to build upon the cybersecurity program.
With the proliferation of cybersecurity breaches, the number of healthcare providers, payers, and business associates investigated by the OCR has risen significantly. It is not unusual for additional penalties to be levied when victims of breaches cannot demonstrate that an enterprise-wide risk assessment exists, comprehensive enough to document all of the risks to ePHI.
Why is it that so many covered entities and business associates fail to comply with this fundamental safeguard? Building a HIPAA Compliant Cybersecurity Program cuts through the confusion and ambiguity of regulatory requirements and provides detailed guidance to help readers:
- Understand and document all known instances where patient data exist
- Know what regulators want and expect from the risk analysis process
- Assess and analyze the level of severity that each risk poses to ePHI
- Focus on the beneficial outcomes of the process: understanding real risks, and optimizing deployment of resources and alignment with business objectives
- Use NIST 800-30 to execute a risk analysis and assessment, which meets the expectations of regulators such as the Office for Civil Rights (OCR)
- Understand why this is not just a compliance exercise,but a way to take back control of protecting ePHI
- Leverage the risk analysis process to improve your cybersecurity program
- Know the value of integrating technical assessments to further define risk management activities
- Employ an iterative process that continuously assesses the environment to identify improvement opportunities
Who This Book Is For
Cybersecurity, privacy, and compliance professionals working for organizations responsible for creating, maintaining, storing, and protecting patient information
The book, Building a HIPAA-Compliant Cybersecurity Program: Using NIST 800-30 and CSF to Secure Protected Health Information [Bulk, Wholesale, Quantity] ISBN#9781484230596 in Paperback by Eric C. Thompson may be ordered in bulk quantities. Minimum starts at 25 copies. Availability based on publisher status and quantity being ordered.
Details
- Publisher
- Apress
- Author
- Eric C. Thompson
- Format
- Paperback
- Published
- Nov 12, 2017
- ISBN-13
- 9781484230596
- Pages
- 297
- Printing
- Printed on demand
Building a HIPAA-Compliant Cybersecurity Program in bulk: pricing
Volume pricing applies automatically in your cart. No codes, no account needed.
| Copies | Price per copy | You save |
|---|---|---|
| 25 – 99 | $45.49 | 30% off list |
| 100 – 249 | $44.19 | 32% off list |
| 250 – 499 | $42.89 | 34% off list |
| 500 – 999 | $41.59 | 36% off list |
| 1,000+ | $40.29 | 38% off list |
Popular for
A copy for every member, on one order.
A book for every attendee, delivered to your venue.
For clients, staff, members or volunteers.
How fast can I get copies of Building a HIPAA-Compliant Cybersecurity Program?
This title is printed on demand, so it needs production time before it ships. Need them by a specific date? Request a quote and we'll confirm timing before you pay.
Can you ship to several locations or people's homes?
Yes. We ship in bulk to one address, to multiple sites, or to individual recipients, in the US and internationally. See fulfillment options.
Can I get a formal quote for approval before ordering?
Yes. Request a quote and we'll send a PDF you can forward for approval.
Do you accept purchase orders and tax-exempt orders?
Yes. We accept purchase orders upon approval, as well as cards, PayPal, ACH, wire transfers and checks. BookPal is a tax-exempt supplier in all 50 states. See purchase orders and sales tax exemption.
What if I find a lower price?
Send us the link. We match prices from other bulk booksellers and distributors on a new copy in the same edition, available to ship in the quantity you need. Clearance sales and pricing errors are the exception, and we'll tell you quickly if that's the case. Start a price match.
Write a Review
Building a HIPAA-Compliant Cybersecurity Program: Using NIST 800-30 and CSF to Secure Protected Health Information
Groups also order

A colleague asked you to approve this order
Your quote list
Add books as you browse, then request one quote for all of them.